Managing Infrastructure At Scale
30 minutes.
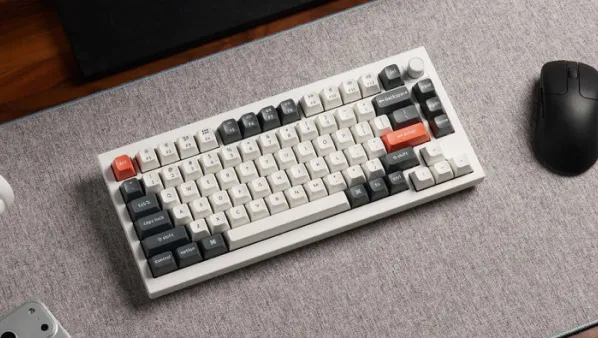
A free keyboard.
A shot at a DGX Spark.
See Terragrunt Scale in action
We'll walk through how Scale solves your specific infrastructure challenges. Bring questions — this is your session.
Get your Keychron keyboard + DGX Spark raffle entry
After the demo, we ship your mechanical keyboard and enter you into the DGX Spark drawing. You can choose any Keychron keyboard up to $150, or we can send you a Keychron gift card to purchase your perfect keyboard.
We generally respond the same business day!
Built for teams that use Terragrunt
Terragrunt gives teams a clean way to organize infrastructure. Terragrunt Scale extends the Terragrunt you already know with a secure, production-grade GitOps workflow—running entirely inside your own GitHub Actions or GitLab CI.
Terragrunt-native GitOps pipelines, drift detection, and automated updates. Review plans in pull requests, apply on merge, minimize blast radius, and keep your units, stacks, and modules aligned with code.
Deploy infra changes with confidence
Deploy safely with Pipelines
Run plans only for affected units, post results back to PRs, and apply on merge in dependency order.
Pipelines supports concurrent runs for independent units, multi-environment changes, HCL-based configuration, and OIDC credentials scoped to each environment.
Detect drift before it becomes an incident
Run scheduled or on-demand scans. When drift is found, open a PR or MR for only the drifted units, review the remediation, and merge when ready.
Start narrow with filtered coverage and expand over time.
Keep IaC current with Patcher
Automatically surface new module, unit, and stack versions as PRs.
Handle breaking changes with patches or clear guidance, reduce noise with grouping, and promote updates from dev to staging to production.
Terragrunt-native GitOps, not retrofitted from generic CI
Runs in your existing GitHub Actions or GitLab CI
Understands Terragrunt units, stacks, and DAGs
Plans and applies only affected units to reduce blast radius
Uses temporary, least-privilege OIDC credentials instead of long-lived secrets
Supports monorepos or polyrepos, GitHub/GitLab, and enterprise/self-managed options
Keeps workflow behavior configurable in HCL instead of hiding it behind a black box

Terragrunt makes managing our infrastructure across providers and environments consistent, safe, and easy to understand. And now with Pipelines, things are even easier… We can literally copy and paste infrastructure and spin up new services, providers, and even full environments in minutes instead of hours or days.